Insights / Cyber Library
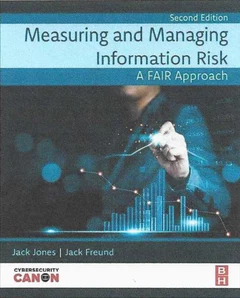
Measuring and Managing Information Risk
A FAIR Approach. Second Edition.
By William J. (Jay) Carson, ISSA Senior Member, Colorado Springs Chapter. Originally published in ISSA Journal’s "The Cyber Library" column, July/August 2026, page 23. ISSA Journal.
Disclaimer: These are the author’s subjective opinions, and do not necessarily reflect the opinions of any organization or individual. A human prepared this article with assistance from Microsoft Editor and Grammarly.
Reviewing the Works of Jack Jones & Jack Freund. Elsevier, (2026).
Measuring and Managing Information Risk: A FAIR Approach. Second Edition.
Sound Bite: Like the Kenny Rogers hit ‘The Gambler,’ you will find many “Aces to Keep” in this book.
Opinion on Primary Audience: Certainly all cybersecurity leaders. If going for an advanced certification like C|CISO, your in-depth knowledge of this topic will give you an edge!
Note: I know one of the authors and he is the editor of the ISSA Journal, but he has no influence over my review.
Think you have ‘risk management’ down so any further mention is boring? I forecast you are wrong! I highly value this book, and there are numerous cybersecurity ‘True Life’ stories. The humor and wisecracks make it read like the authors are talking to you over a beer and drawing the diagrams on bar napkins. All the serious players will read and value it, but it also would be a wonderful information risk baseline text if authoring a cyber novel like The Phoenix Project!
A tip on reading this book: There are a lot of abbreviations in Factor Analysis of Information Risk (FAIR). I made my bookmark a 3×5 card listing Loss Event Frequency (LEF), Loss Magnitude (LM) Threat Event Frequency (TEF), Threat Agent Library (TAL), Threat Capability (TCap), Variance Duration (VD), Variance Management (VM), Variance Frequency (VF), Loss Event Control (LEC), Decision Support (DS), and Resistance Strength (RS). It makes it easier to keep your reading with understanding up!
The Authors: Probably smartest people on FAIR. Jack Jones is a Risk Management Executive on the faculty at the Institute of Applied Network Security and an adjunct professor at Carnegie Mellon. BS in Cybersecurity. He has the CRISC certification from ISACA. Prestigious awards. Jack Freund is a Distinguished Fellow of ISSA, a Fellow of IAPP and the FAIR Institute. PhD in Information Systems. CISSP, plus too many other certifications to list. He is the editor of the ISSA Journal.
The Metadata: Ordering a copy online will cost about $60, even for an electronic copy. Probably no public library copies. Using a Wikipedia article on Flesch-Kinkaid Readability, it is college level (one page sample), about 19% passive voice. This article is 3% passive voice.
Table of Contents (Excerpts)
[Including Reviewer notes]
- Basic Risk Concepts and Misperceptions [You will say Aha!]
- FAIR Terminology [Not hard, but important]
- Measurement [Dealing with uncertainty]
- Analysis Process [Watch your asset]
- Common Mistakes [Susceptibility analysis, et al]
- Standards and Regulatory Alignment [Important]